A payment that arrives in seconds can still reach the wrong person. For families sending money abroad and businesses paying overseas suppliers, speed answers only part of the question. The harder test is whether the system can establish who is involved, recognize when something is wrong, and assign responsibility when protection fails.
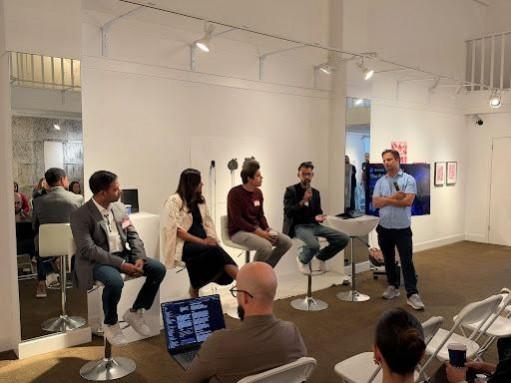
Those questions were central to a discussion at SF Tech Week in San Francisco. At Zennopay’s October 7 panel, “The Future of Global Money Movement,” Consulting manager and AI in Compliance practitioner Nikhil Mittal joined Oneal Bhambani, founder and chief executive officer of Flyra and former chief financial officer of Flutterwave, and Kranthi Meka, who works in partnerships at Thunes and previously worked at Visa.
The discussion covered evolving payment infrastructure, local payment networks, and the obstacles to seamless cross-border transfers. In his commentary published after the panel, Nikhil developed a related argument: financial crime compliance belongs inside payment infrastructure, not at a checkpoint added after the system is built.
Speed Does Not Establish Legitimacy
Nikhil Mittal brings more than 19 years of financial crime compliance experience. Now a consulting manager at one of the Big Four advisory firms, working on artificial intelligence (AI) in compliance, he brings experience in transaction-monitoring analytics, customer risk models, sanctions-screening systems, and compliance transformations for major financial institutions. He also holds a Master of Business Administration from Duke University’s Fuqua School of Business.
That experience informs an important distinction in his commentary: a payment can be technically successful without being legitimate. Strong reserves do not prevent a stablecoin from carrying fraud proceeds, just as a customer’s successful onboarding does not guarantee that later activity remains lawful.
Anti-money laundering controls address efforts to disguise illicit funds. Sanctions controls address prohibited dealings, while fraud controls help identify deception and misuse.
Local payment rails, the domestic networks used to move funds, are part of the problem, not separate from it. Nikhil’s premise was that global payments remain fragmented across those networks, currency conversion, liquidity, compliance, settlement, and reconciliation. Connecting two networks therefore requires more than making their technology communicate. In his view, providers also need clear arrangements for the information and responsibility that accompany a payment.
Build Controls Around Every Handoff
Nikhil’s proposed approach starts before a transaction moves. Providers should identify the participants in the payment journey, the jurisdictions involved, and each institution’s or service provider’s responsibilities.
At onboarding, that means conducting risk-based identity checks, understanding business ownership, and, where appropriate, assessing counterparties and wallet relationships. A wallet address is a destination, not proof of its controller’s legal identity a distinction that makes wallet due diligence different from merely checking whether an address can receive funds.
The next challenge is preserving useful information as value moves. For providers, information exchange must work in practice: they must use data, recognize exceptions, and know how to resolve them.
In this case, Nikhil proposes combining applicable sanctions controls with fraud indicators, beneficiary checks, customer behavior, and transaction context. The objective is a governed decision: proceed, seek more information, investigate, or intervene where required and legally permitted.
His practitioner background is relevant here. Nikhil describes building case-management platforms for two multinational banks and connecting analytics with the needs of compliance and investigation teams.
He advocates connecting lawfully available information across transfers, accounts, devices, counterparties, and redemption activity, with AI and network analytics supporting investigations rather than replacing judgment. The lesson is operational: faster detection has limited value if the institution cannot respond while intervention is still possible.
Accountability Across Borders
Nikhil identifies four gaps that faster infrastructure alone cannot resolve: fragmented cross-border obligations, unclear responsibility between providers, inconsistent information sharing, and limited recovery options after fraud.
Together, these gaps highlight a distinction payment providers cannot afford to overlook: settlement speed alone cannot measure progress; at the same time, connecting financial networks does not automatically connect the safeguards around them. Providers must reconcile requirements governing customer information, sanctions screening, and data storage and transfer, sometimes across conflicting legal frameworks.
Responsibility becomes more complicated when several providers handle different stages of the same payment. Each participant may understand its own role, yet the arrangement still needs to establish who investigates missing information, communicates a fraud warning, or coordinates an intervention.
Information sharing presents a related difficulty. Collecting more data is not enough if another provider cannot lawfully access it or interpret it consistently. Nikhil therefore emphasizes compatible data requirements and clear legal pathways for exchanging payment information while maintaining privacy protections.
However, accountability must extend beyond fraud detection. Providers need clear arrangements to investigate reports, coordinate with other institutions, and pursue recovery where possible, especially when a payment crosses borders and no single institution controls its entire journey.
Nikhil clarifies that in these situations, it does not mean every loss can be reversed. Rather, it means customers should know who is handling their case, what action is being taken, and what options remain. Providers should establish these responsibilities before an incident, rather than leaving the customer to navigate disconnected organizations afterward.
Guardrails for the Next Phase
As payment systems get faster and more interconnected, strong compliance should help institutions make better decisions, not shift the burden of poor design onto everyone using the service. They must also prompt new questions: where could information disappear, which institution could recognize abuse, and what happens if a legitimate payment is wrongly stopped?
For financial compliance leaders such as Nikhil Mittal, the responsibility is forward-looking: examine emerging payment models, anticipate how they could be exploited, and revisit controls as real-world cases reveal weaknesses. The goal is to ensure that each advance in moving money is matched by a credible ability to protect it and to respond when protection fails.
Nikhil mentions, “That is the role of financial crime compliance: making global connectivity something customers and institutions can trust.”